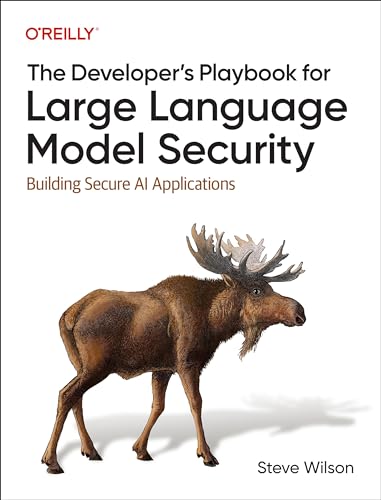
Large language models (LLMs) are not just shaping the trajectory of AI, they're also unveiling a new era of security challenges. This practical book takes you straight to the heart of these threats. Author Steve Wilson, chief product officer at Exabeam, focuses exclusively on LLMs, eschewing generalized AI security to delve into the unique characteristics and vulnerabilities inherent in these models.
Complete with collective wisdom gained from the creation of the OWASP Top 10 for LLMs list—a feat accomplished by more than 400 industry experts—this guide delivers real-world guidance and practical strategies to help developers and security teams grapple with the realities of LLM applications. Whether you're architecting a new application or adding AI features to an existing one, this book is your go-to resource for mastering the security landscape of the next frontier in AI.
You'll
Why LLMs present unique security challenges How to navigate the many risk conditions associated with using LLM technology How to identify the top risks and vulnerabilities associated with LLMs Methods for deploying defenses to protect against attacks on top vulnerabilities And more!
Good general overview of LLM security. Has a good approach of viewing security in terms of a software supply chain, which then allows a generalization of supply chain risks to the software domain. General, but it is a "playbook" as the title says.
“LLM Application Security” is a serious attempt to organize the risks, threats, and protection methods for systems that use large language models (LLMs). The author takes on a tough job-explaining a fast-changing and still quite new field-in a step-by-step, example-based way, with a strong focus on real-world practice.
What I liked most were the many clear examples that make it easier to understand how attacks work and how to prevent them. The writing style reminded me of Adam Shostack’s famous book on threat modeling - both authors break things down clearly, using real cases to explain each type of threat. This is a big strength of the book.
The book doesn’t try to be trendy- it’s reliable and practical. It feels more like a solid training guide than a popular science book. But thanks to all the examples, it’s not boring. It feels like a smart colleague explaining a threat to you on a whiteboard, then showing you two real-life cases and a counterexample to help you understand the limits.
In fact, the book contains many topics, but it gives foundational knowledge about AI. For me, this book took much longer than I expected, because after each chapter I did a knowledge check and made some notes. However, the book will definitely be useful both for people who have no idea about LLMs but would like to somehow start becoming interested in this field, and for those who are already somehow related with LLMs. There are many good insights, thoughts, and recommendations in the book that are worth paying attention to, but probably the most important thing that is worth understanding throughout the whole book is that "with great power comes great responsibility", and LLMs are no exception in this case, because with the help of AI we are able to automate and simplify our lives and tasks, but we should also take care of its security in order to protect the world from negative consequences.
Many rules of thumb for secure development and deployment of Large Language Models based on common sense, as well as some rules inferred from non-AI computer security. Maybe this is one of the first books of its kind?
The book offers a good understanding of the many attack vectors a LLM faces. It not only shows how things can go bad, but what we can do to mitigate and reduce the attack surface. Definitely a must-read for everyone who puts an LLM in the world.