

What do you think?
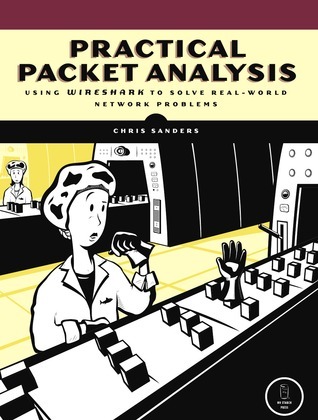
Practical Packet Analysis: Using Wireshark to Solve Real-World Network Problems
It's easy enough to install Wireshark and begin capturing packets off the wire--or from the air. But how do you interpret those packets once you've captured them? And how can those packets help you to better understand what's going on under the hood of your network? Practical Packet Analysis shows how to use Wireshark to capture and then analyze packets as you take an indepth look at real-world packet analysis and network troubleshooting. The way the pros do it.
Wireshark (derived from the Ethereal project), has become the world's most popular network sniffing application. But while Wireshark comes with documentation, there's not a whole lot of information to show you how to use it in real-world scenarios. Practical Packet Analysis shows you how
Because net-centric computing requires a deep understanding of network communication at the packet level, Practical Packet Analysis is a must have for any network technician, administrator, or engineer troubleshooting network problems of any kind.
Wireshark (derived from the Ethereal project), has become the world's most popular network sniffing application. But while Wireshark comes with documentation, there's not a whole lot of information to show you how to use it in real-world scenarios. Practical Packet Analysis shows you how
Because net-centric computing requires a deep understanding of network communication at the packet level, Practical Packet Analysis is a must have for any network technician, administrator, or engineer troubleshooting network problems of any kind.
192 pages, Paperback
First published May 23, 2007
Ratings & Reviews
Friends & Following
Create a free account to discover what your friends think of this book!
Community Reviews
Displaying 1 - 30 of 36 reviews

September 13, 2011
Wireshark is one of the more useful tools available for people doing network packet analysis. But a tool is good if you know how to use it and this books show you how to use it in an easy to follow practical guide.
After going through an introduction to network packet analysis and using Wireshark, the book gets down to the nitty-gritty: using Wireshark to troubleshoot networks. You'll learn how to determine where a network problem might be happening and how to backup your analysis with evidence gathered using Wireshark.
One part that definitely needs more work is the section on wireless network analysis. This is an especially challenging part of a network to troubleshoot due to the difficulty of getting proper hardware to capture wireless packets, much less ensuring that you are getting the data you need to do proper analysis. What is covered in this book is enough to get you started in wireless network analysis but more coverage of this topic would be helpful.
After going through an introduction to network packet analysis and using Wireshark, the book gets down to the nitty-gritty: using Wireshark to troubleshoot networks. You'll learn how to determine where a network problem might be happening and how to backup your analysis with evidence gathered using Wireshark.
One part that definitely needs more work is the section on wireless network analysis. This is an especially challenging part of a network to troubleshoot due to the difficulty of getting proper hardware to capture wireless packets, much less ensuring that you are getting the data you need to do proper analysis. What is covered in this book is enough to get you started in wireless network analysis but more coverage of this topic would be helpful.

November 19, 2022
Between 3 and 4 stars. This book is an entry level, thus if you have little experience with networks you will actually enjoy it a lot. It's short but has nice breadth of coverage, it explains basics of OSI and tcp in a very non-frighting way. And the fact that you can check theory by looking at real network packets is awesome.
The best part of the book is practical examples of troubleshooting connection issues, performance problems and security threats. Most examples are basic but because the book is accompanied with pcap files it's actually good at teaching how to work with packet dumps on a small scale. You can always try to figure things out by yourself before reading the explanation in the book.
I've picked it up to learn some tricks of wireshark, as far as the "user guide" it's again entry level but the book forced me to look closer at "Statistics" menu and I don't regret reading it.
The best part of the book is practical examples of troubleshooting connection issues, performance problems and security threats. Most examples are basic but because the book is accompanied with pcap files it's actually good at teaching how to work with packet dumps on a small scale. You can always try to figure things out by yourself before reading the explanation in the book.
I've picked it up to learn some tricks of wireshark, as far as the "user guide" it's again entry level but the book forced me to look closer at "Statistics" menu and I don't regret reading it.
November 17, 2024
A productive read.
I've been familiar with Wireshark and basic filtering. What I gained from this read, however, was a cognitive expansion into all the different ways I could use Wireshark to analyze a network—everything from a basic revision of the OSI stack to use cases in which one might find themselves needing to debug network-related issues (latency, intrusion, malware, etc.).
I was hoping to find ways to use Wireshark for more use cases at the physical level of the OSI stack, and there was a bit of that, albeit most of which was condensed within a single chapter relegated to Wireless communications. It was fine, I just wish there was more of that stuff.
I've been familiar with Wireshark and basic filtering. What I gained from this read, however, was a cognitive expansion into all the different ways I could use Wireshark to analyze a network—everything from a basic revision of the OSI stack to use cases in which one might find themselves needing to debug network-related issues (latency, intrusion, malware, etc.).
I was hoping to find ways to use Wireshark for more use cases at the physical level of the OSI stack, and there was a bit of that, albeit most of which was condensed within a single chapter relegated to Wireless communications. It was fine, I just wish there was more of that stuff.
October 19, 2017
Great book for anyone who is interested in how the Internet and its different protocols work.
Highly recommend that you download the packet capture files from their website and try everything yourself as you read this book.
I'm sure I will keep coming back to this book over and over again.
Highly recommend that you download the packet capture files from their website and try everything yourself as you read this book.
I'm sure I will keep coming back to this book over and over again.
June 10, 2019
This was a great intro to basic network analysis, for those without a lot of background in networking, or who might be a bit rusty in this area. Personally, I'm a DevOps guy with more experience on the Dev than Ops side. I'm working on skilling up, in an effort to close that gap. While most of the low level networking nuts & bolts described here are abstracted away enough in my current cloud-based role, that I might not need these skills on a daily basis, a little more robust networking knowledge certainly can't hurt.
February 4, 2020
Good book that gives you an overview of network concepts, as well as some really good hands on experience with analysing packets in Wireshark, which is where it really shines. It's a great practical guide. Would recommend to people interested in understanding and analysing network traffic better.
May 14, 2025
This book is one of the best introductions to networking. It’s clearly written, offers a solid grasp of key concepts, and enhances learning with practical, real-world examples—making even complex topics accessible.
September 4, 2017
This was one of the best "tech" books I've ever read. It really flows well, and the explanation is clear and concise. I'm blown away.
March 15, 2018
Was able to get me up and running with some of the most useful Wireshark features while also giving some background into networking.
March 15, 2019
Good book. Provides in depth knowledge on Wireshark and networking.

February 21, 2020
Excellent book. The author did his research on this one. Would probably use for reference.
Want to Read
July 19, 2020elibrary
Read
September 27, 2020Was ok - was hoping for some more exercises a la malware-traffic-analysis.net, but there were none. Most of this info is pretty easy to learn online, but the book is still a good contribution.
February 22, 2022
Great book to grasp the fundamentals of packet analysis using Wireshark
March 15, 2023
Te enseña las bases de wireshark usando ejemplos reales. Muy bueno

December 21, 2023
The book gives practical tips on working with Wireshark. The examples are clear and simple.
There aren't enough exercises to work on polishing your skills, though.
There aren't enough exercises to work on polishing your skills, though.
May 1, 2009
I really wanted to like this book.
The first few chapters give a quick summary of networking and TCP/IP basics. It's a subject which is difficult to cover so quickly. I'm not sure Sanders does it justice, to be honest--if you aren't already familiar with the concepts, I don't think this would be an adequate introduction.
The next few chapters discuss the mechanics of using the Wireshark program itself. I appreciate this section, as it taught me a few simple but very useful features of Wireshark that I had overlooked.
The bulk of the book presents a few packet capture use cases, and guides you through the analysis. You can download the .pcap files and follow along, and I encourage you to do that. Some of the examples can be puzzled out from the packet captures alone, and these are pretty fun. Unfortunately, a lot of the examples are only given a superficial treatment. I already knew that bittorrent traffic can consume a lot of bandwidth and will go all over the place, and the idea to look for the word bittorrent in the traffic itself is not all that insightful.
But the real letdown is the errors: the first printing has a ton of them. Things like the wrong diagram, or a packet trace that has obviously incorrect MAC addresses. On Amazon, the author says that many of these errors were corrected in later printings, but that doesn't help me. As of today, a year after he made that comment, there's still no errata for the first edition on the No Starch Press website.
The first few chapters give a quick summary of networking and TCP/IP basics. It's a subject which is difficult to cover so quickly. I'm not sure Sanders does it justice, to be honest--if you aren't already familiar with the concepts, I don't think this would be an adequate introduction.
The next few chapters discuss the mechanics of using the Wireshark program itself. I appreciate this section, as it taught me a few simple but very useful features of Wireshark that I had overlooked.
The bulk of the book presents a few packet capture use cases, and guides you through the analysis. You can download the .pcap files and follow along, and I encourage you to do that. Some of the examples can be puzzled out from the packet captures alone, and these are pretty fun. Unfortunately, a lot of the examples are only given a superficial treatment. I already knew that bittorrent traffic can consume a lot of bandwidth and will go all over the place, and the idea to look for the word bittorrent in the traffic itself is not all that insightful.
But the real letdown is the errors: the first printing has a ton of them. Things like the wrong diagram, or a packet trace that has obviously incorrect MAC addresses. On Amazon, the author says that many of these errors were corrected in later printings, but that doesn't help me. As of today, a year after he made that comment, there's still no errata for the first edition on the No Starch Press website.
June 3, 2012
This isn't a bad tech read. Chris keeps it simple and to the point. A book like this is more of less what I would call a temporary reference book. His examples are great,however, once you refer to them two or three times you will either have outgrown their usefullness or wireshark will have become outdated. Either way, I highly recommend this book for anyone who does networking for a living.

March 23, 2014
Decent book if you're interested in packet analysis with Wireshark and looking for some practical examples. I would recommend that book for a beginner rather than a experienced professional since you're probably know most things already if you played with wireshark and do some analysis.
January 31, 2017
Książka ma już parę lat, ale w większości jest aktualna. W sumie internet, a tak naprawdę jego początki sięgają lat 60., ale protokoły tcp/ip za bardzo się nie zmienił. Tak jak w tytule główny nacisk jest nastawiony na Wireshark. Jeżeli miałeś styczność z siecią, nie będzie to dla Ciebie problem.

December 2, 2007
The first half of this book reads like an extended help file. What makes up for it are the interesting case studies where the author shows you how to use Wireshark to solve real network crises.

December 19, 2012
Nice basic introduction to packet analysis using Wireshark.

May 21, 2013
Excellent resource for getting deeper into Packet Analysis. Case studies helped, some errors though.
May 28, 2013
Good, but could have gone a bit deeper
June 3, 2013
This book is so incredibly useful. It really is practical and as long as you pay attention and use the examples it will explain wireshark perfectly.
January 7, 2014
Easy enough read for beginners while manages to get your feet wet In advanced topics.

July 17, 2014
Excellent resource for network analysts.

October 20, 2014
This was a very basic introduction. had a few practical examples.
Please let me know if you know of a technical book that actually analyzes packets in depth.
Please let me know if you know of a technical book that actually analyzes packets in depth.
February 11, 2015
I liked the sections dealing with every day problems and how to use Wireshark to trace them to determine where the problem exits.
June 15, 2015
great I love this book
Displaying 1 - 30 of 36 reviews